Identity for every user,
app and AI agent
Casdoor secures how customers, employees and AI agents sign in and what they can access: single sign-on, MFA, passwordless login and fine-grained authorization, on open standards. Run it in your own data center or on a dedicated Casdoor Cloud instance.
Cloud from $25/month with no per-user fees · or self-host for free →
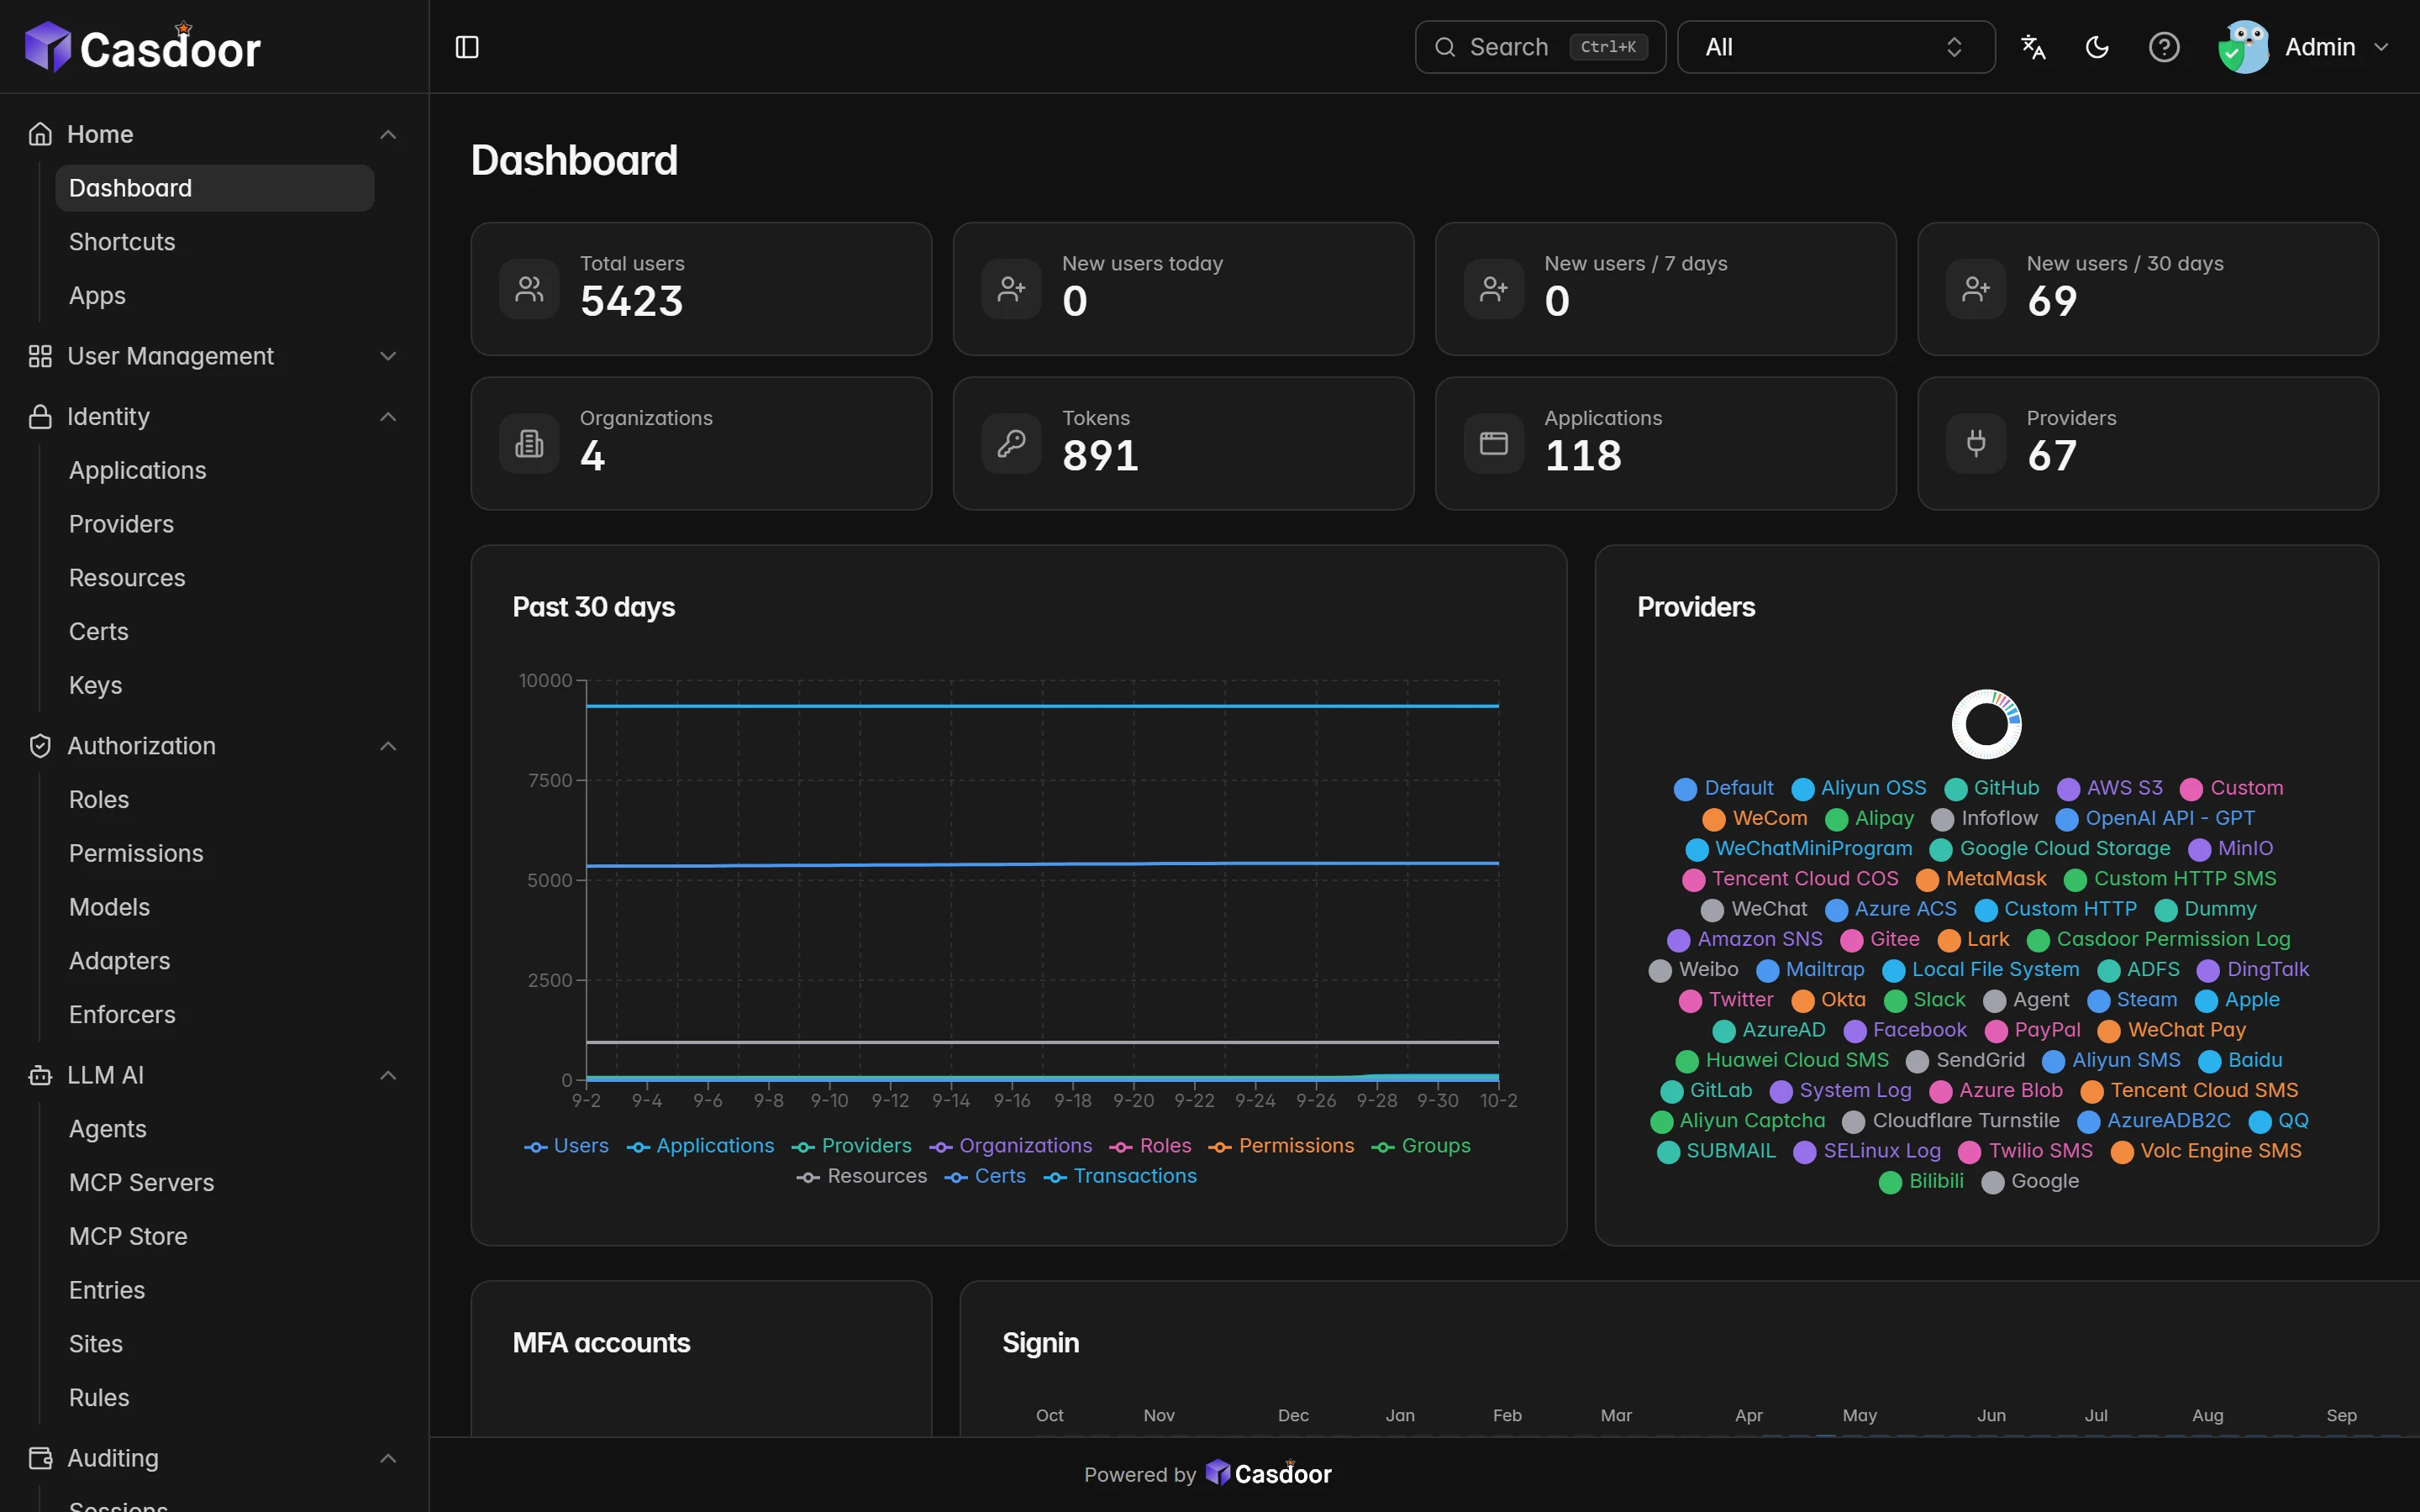
Built into products and platforms from leading AI companies, enterprises and Apache projects




Casbin, the authorization engine inside Casdoor, runs in code from


Proven in production, on every continent
From start-ups to banks, carmakers and ministries of education, teams run their sign-in on Casdoor, in the cloud or behind their own firewall.
- Active login domains
- 5,000+
- with a live Casdoor login page in the last 90 days*
- Login page loads a month
- 1.5M+
- across those deployments, September 2026*
- Docker pulls
- 2.2M+
- of the official Casdoor images
- GitHub stars
- 14.5k
- one of the most-starred open-source IAM projects
* Counted from requests to Casdoor's public CDN, July to September 2026. Deployments that host their own assets or run on private networks are not included, so the real numbers are higher.
The Casdoor platform
One identity platform. Every kind of identity.
Customers, employees, partners and AI agents sign in through the same open-source server, with one console, one audit trail and one bill.
Customer identity
Sign-up and login your users actually finish
Hosted, fully branded login pages with passwordless, social login and MFA, plus self-service profiles and built-in billing.
- Passkeys, magic links and one-time codes
- 75+ social and enterprise providers
- Plans, subscriptions and payments
Workforce identity
One login for every employee app
Single sign-on for SaaS and in-house apps, with a directory that also speaks the protocols your VPN, Wi-Fi and legacy systems need.
- SAML, OIDC and CAS single sign-on
- Built-in LDAP, RADIUS and Kerberos
- SCIM, AD, WeCom and DingTalk sync
AI agent identity
Let AI agents act, with permission
Put OAuth in front of your MCP servers, register AI clients automatically and give every agent scoped, short-lived, auditable access.
- MCP authorization out of the box
- Dynamic client registration
- Token Exchange and DPoP
Authorization
Permissions as a service, powered by Casbin
Model who can do what with ACL, RBAC or ABAC, manage it in the console and enforce it from any service with one API call.
- Roles, groups and resource policies
- Time-limited permissions
- See why a user has each permission
Solutions
Built for what you're building
Whatever you ship, Casdoor handles identity the same way: standard protocols, one console and SDKs for your stack.
Ship AI agents without giving away the keys
Make Casdoor the authorization server for your MCP servers. AI clients such as Claude, ChatGPT and Cursor discover it, register themselves and get tokens scoped to the tools a user allowed, and every call is logged.
Featured capabilities
{
  "resource": "https://mcp.acme.com",
  "authorization_servers": ["https://door.acme.com"],
  "scopes_supported": ["tickets:read", "tickets:write"],
  "bearer_methods_supported": ["header"]
}

// The MCP client finds Casdoor here, registers itself (RFC 7591)
// and asks for a token for https://mcp.acme.com (RFC 8707).Identity for AI agents
Secure the agentic future, on open standards
AI agents now read your tickets, query your data and call your APIs. Casdoor gives every agent a verifiable identity and lets your users decide exactly what it may do, using the same OAuth standards the MCP specification is built on.
- 1DiscoverRFC 9728
The AI client calls your MCP server and finds Casdoor in its protected resource metadata.
- 2RegisterRFC 7591
The client registers itself with Casdoor. No API keys to copy around.
- 3ConsentOAuth 2.1 + PKCE
The user signs in and approves only the tools and scopes the agent needs.
- 4ActRFC 8707 · DPoP
The agent gets a short-lived token for that one server, bound to its key.
An MCP store for your organization
Browse ready-made MCP servers, add the ones your teams need with one click, and manage them next to your applications. Casdoor syncs each server's tools so you can decide exactly which ones agents may call.
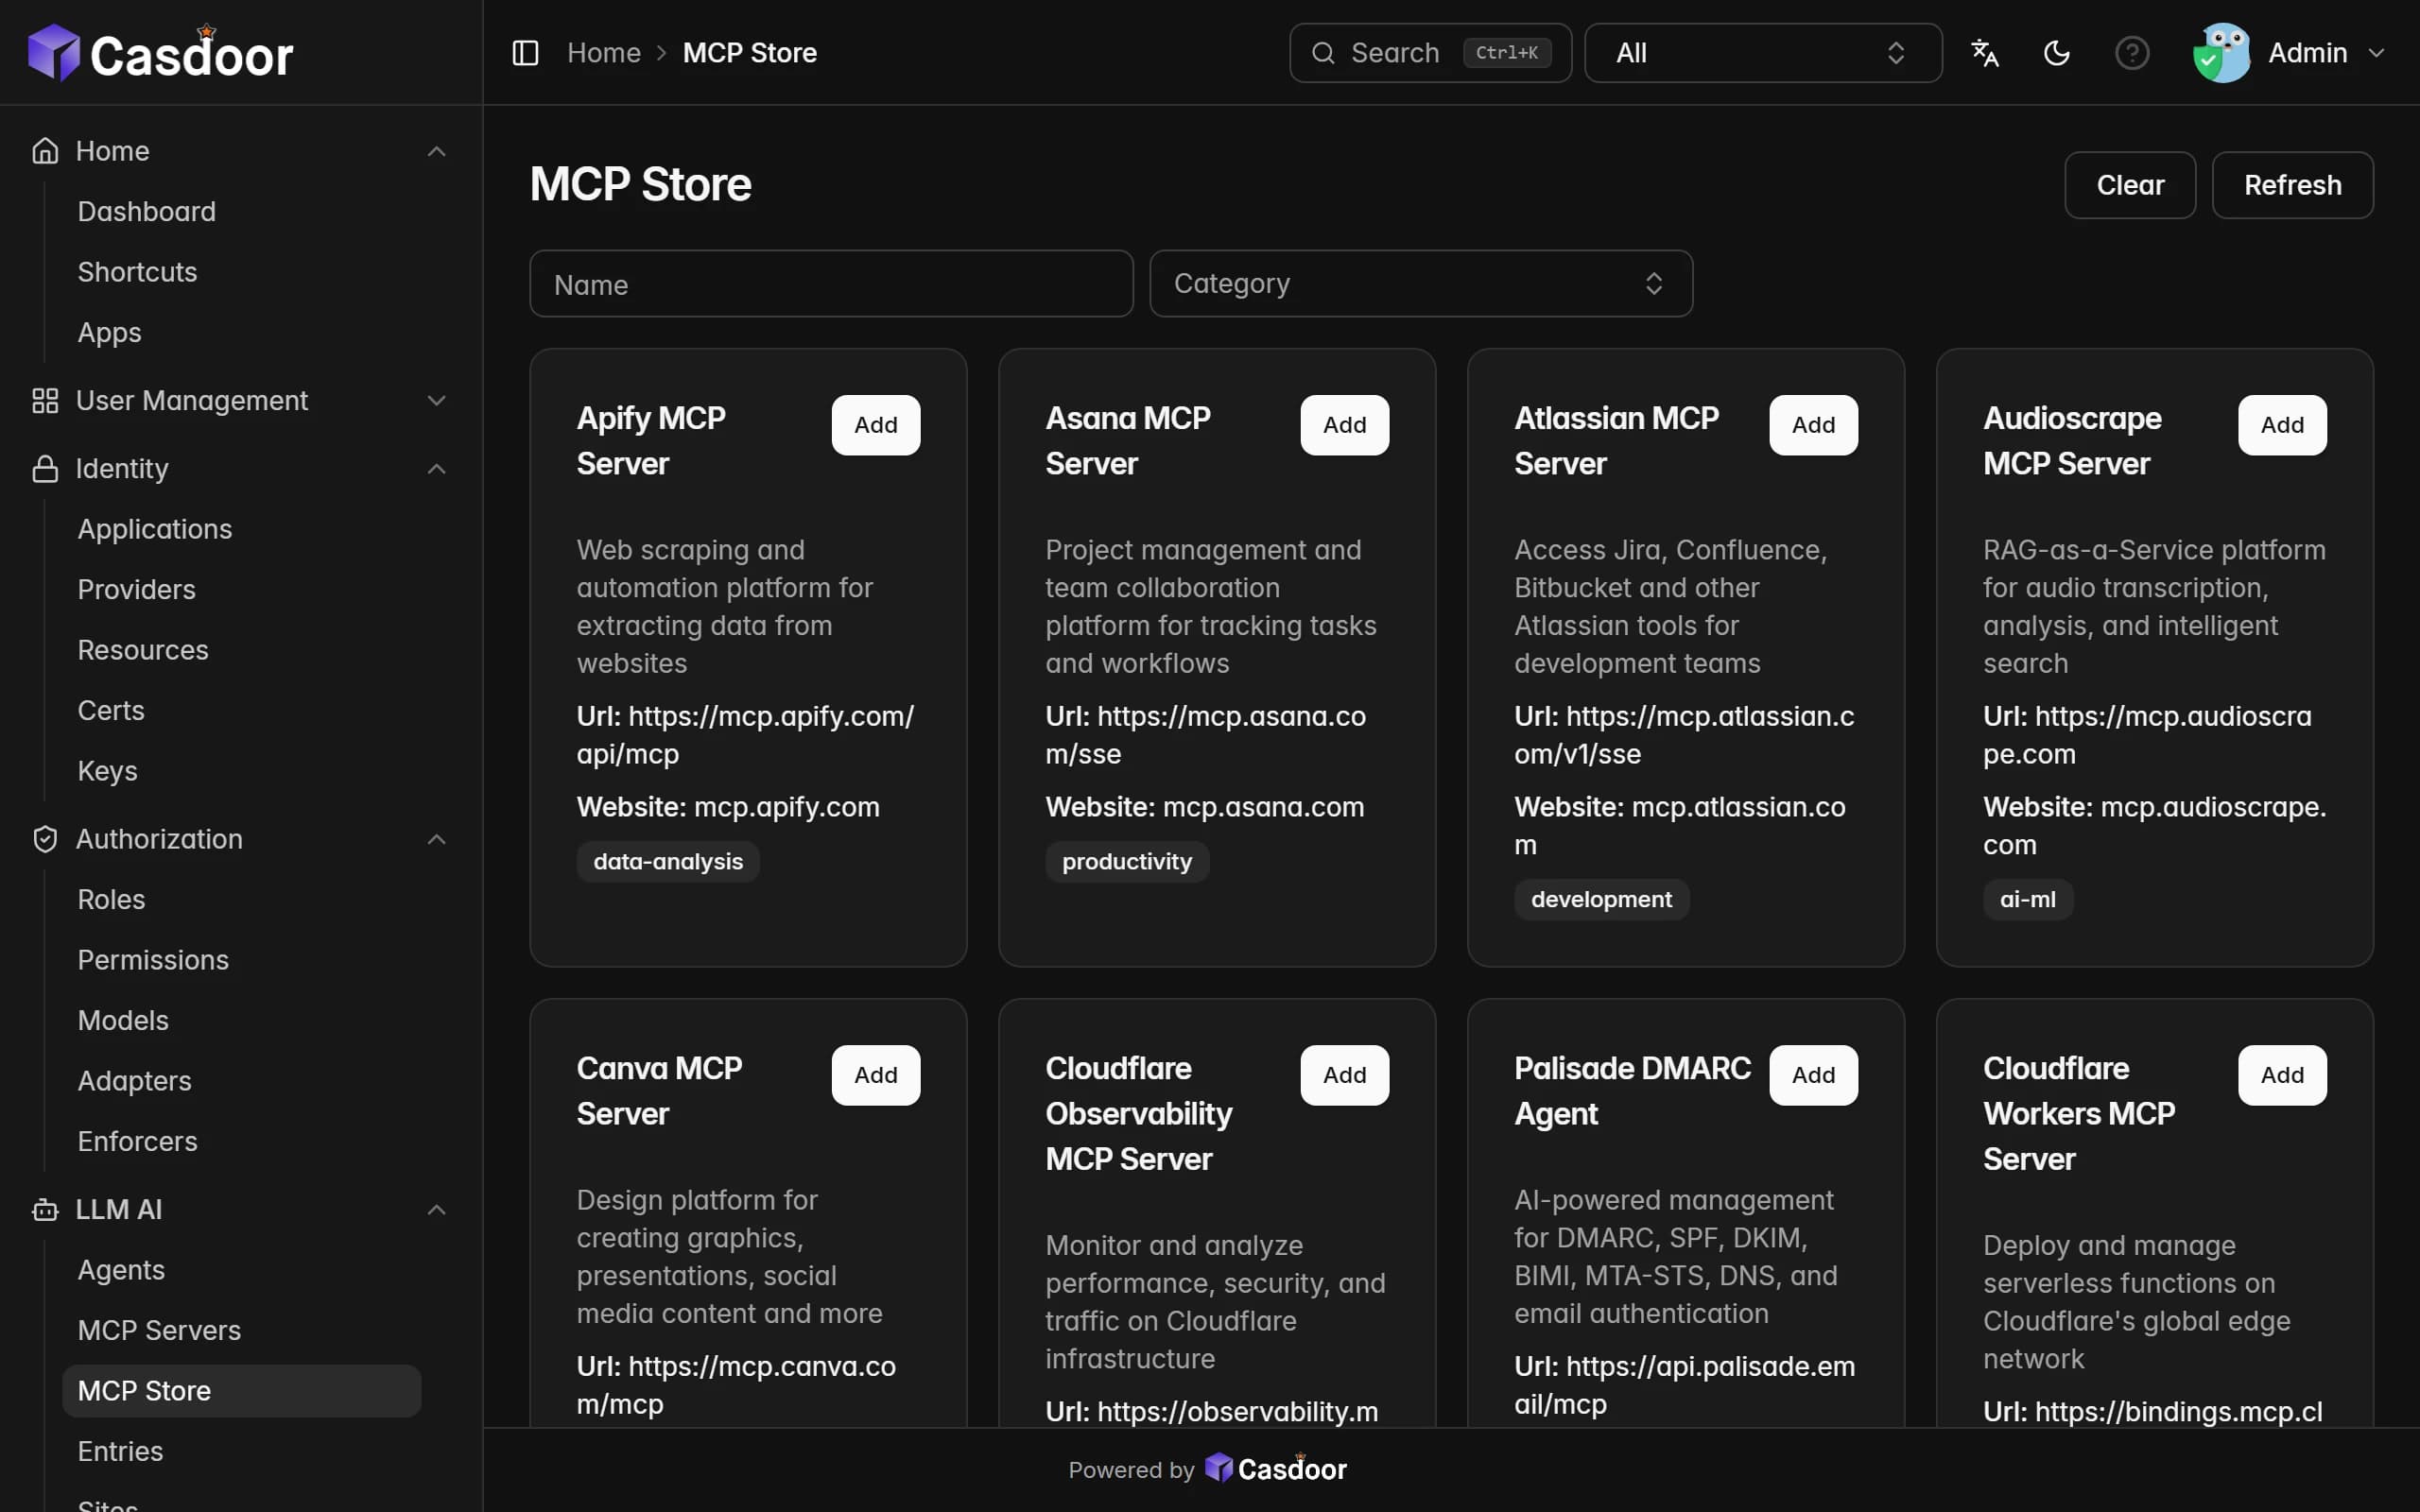
MCP server registry
List your MCP servers, sync their tools and decide which tools each application may call.
Find shadow MCP servers
Scan your internal network for MCP servers nobody registered, before an agent finds them.
Delegation, not impersonation
Token Exchange lets an agent act on a user's behalf with a narrower, traceable token.
Every action on record
Agent sign-ins and API calls land in the same audit trail as people, and can stream to your SIEM.
Capabilities
Everything an identity team needs. Nothing to bolt on.
Casdoor is one server with one console. Every capability below is included, in Casdoor Cloud and in the free open-source edition.
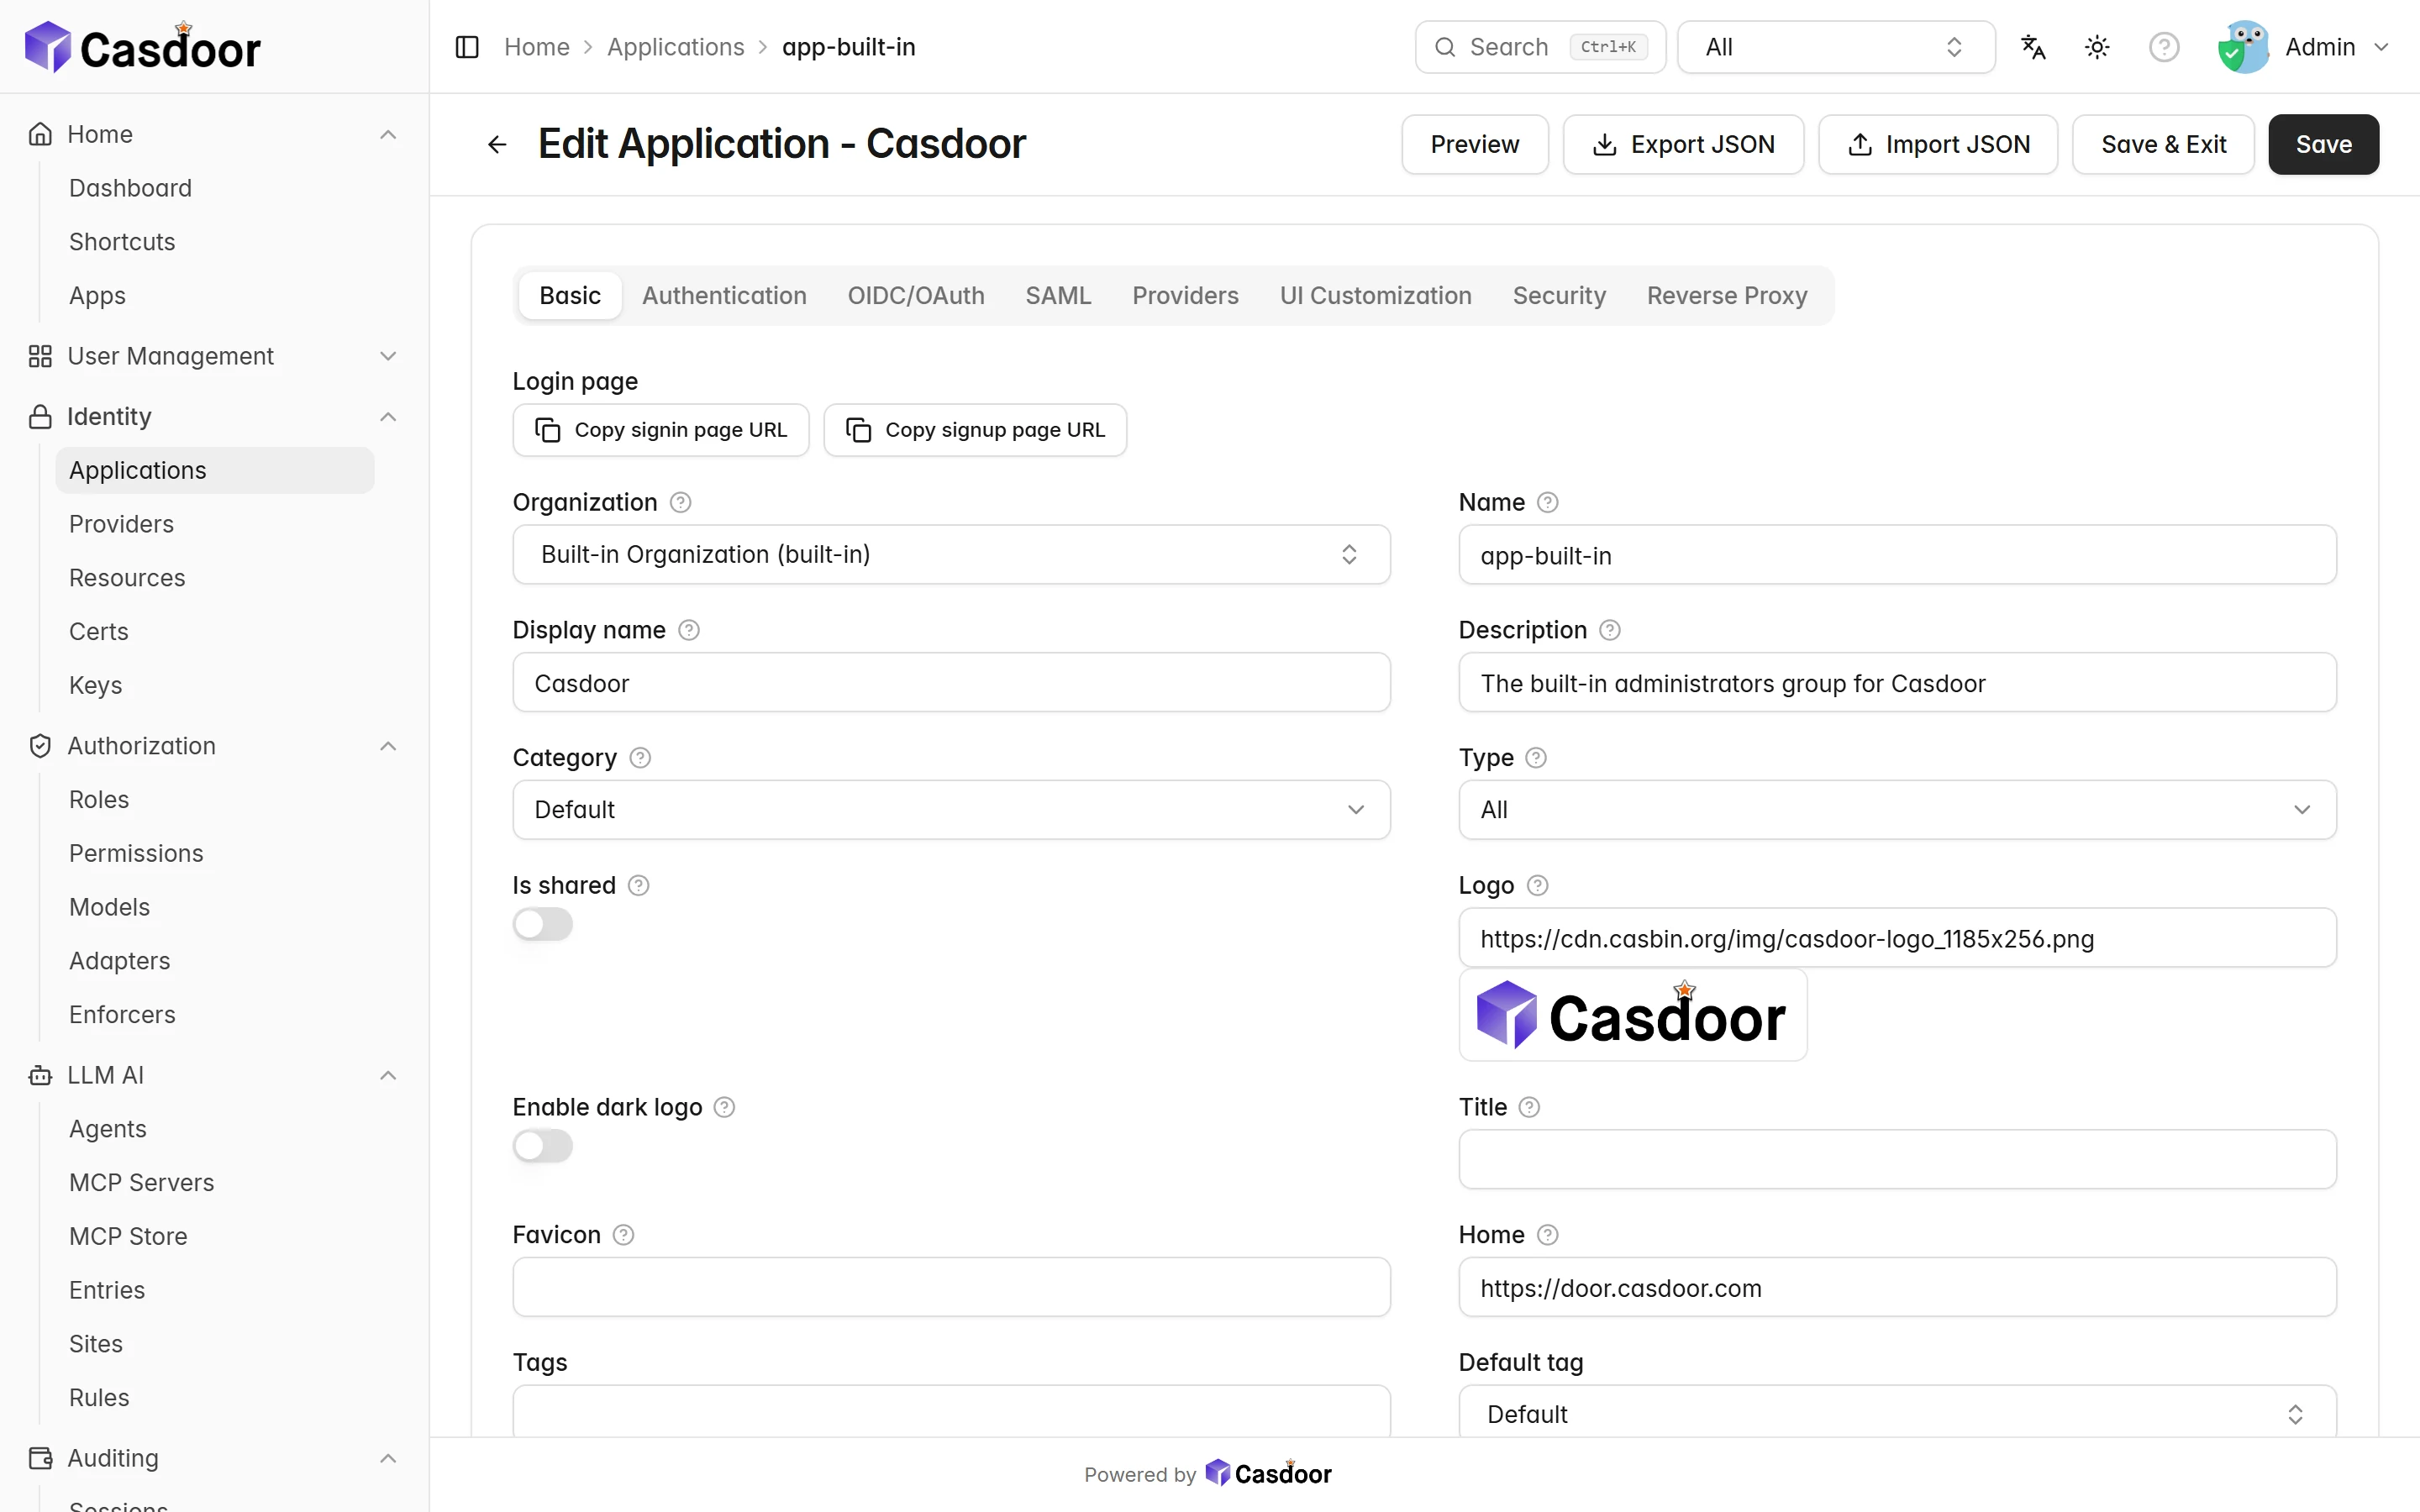
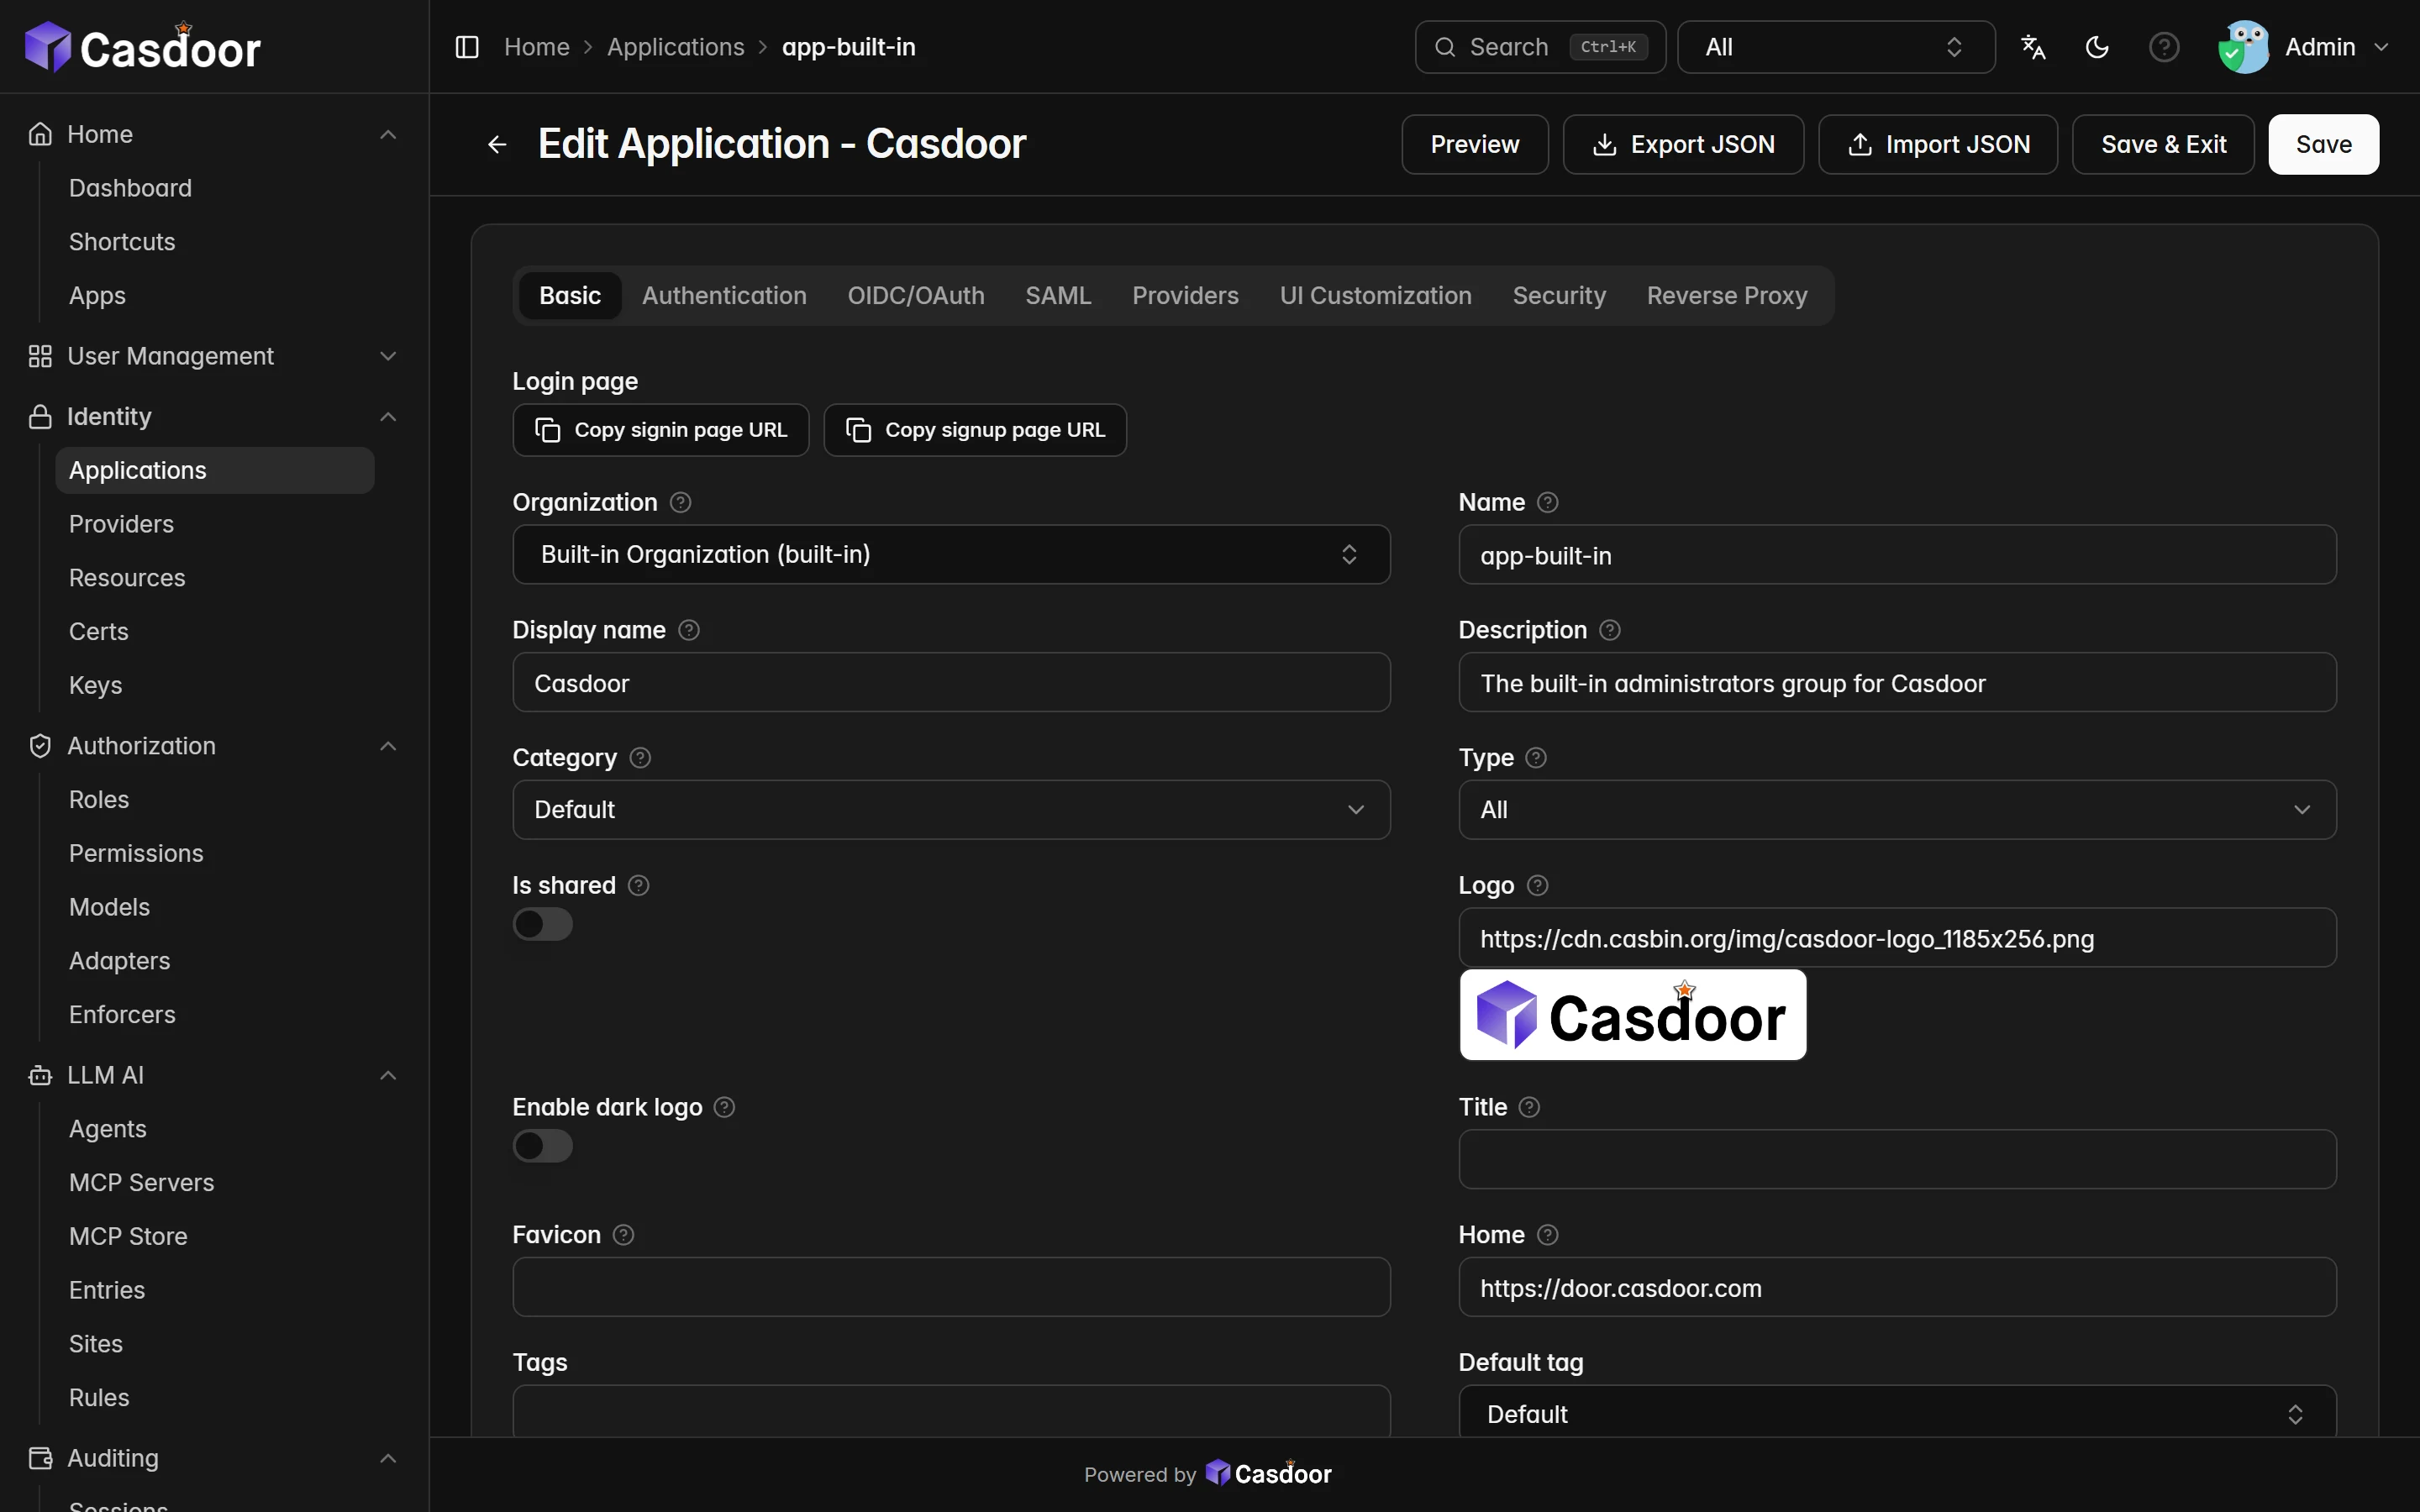
Authentication
- Hosted, brandable login and sign-up pages
- Passkeys (WebAuthn), Face ID and magic links
- TOTP, SMS, email and RADIUS MFA, required per organization
- 75+ social and enterprise identity providers
- reCAPTCHA, hCaptcha, Turnstile and GeeTest
- Password policies with history checks
Single sign-on & protocols
- OAuth 2.0 and OpenID Connect provider, with PKCE
- SAML 2.0 IdP with Single Logout and IdP-initiated SSO
- CAS, LDAP, RADIUS and Kerberos/SPNEGO
- Upstream OIDC and SAML: Entra ID, Okta, ADFS
- Device flow, Token Exchange, DPoP, JWT client auth
- Back-channel and RP-initiated logout
Authorization
- Casbin models: ACL, RBAC, ABAC or your own
- Roles, groups and per-resource permissions
- Single and batch enforce APIs
- Permissions that expire automatically
- See which role or group granted each permission
- Per-tool permissions for MCP servers
Users & directory
- Organizations with their own users, apps and branding
- Group trees, invitations and bulk import or export
- SCIM 2.0 provisioning API
- Sync from Active Directory, Entra ID, Google Workspace and Okta
- Keycloak, AWS IAM, SCIM, WeCom, DingTalk, Lark and database syncers
- Self-service account pages and impersonation for support
Extend & integrate
- REST API and Swagger docs for every object
- 20+ official SDKs for web, backend, mobile and desktop
- Webhooks for sign-ins, sign-ups and changes
- Custom HTML and CSS on login pages
- Built-in payments, plans and subscriptions
- Email, SMS, storage and notification providers
Operations
- Audit records, forwarded to Syslog and your SIEM
- Session list with device and IP, and session limits
- Retention settings for records and tokens
- MySQL, PostgreSQL and other databases
- Docker, Helm chart and Redis Cluster for HA
- 11 interface languages
What's new
Shipping every week, in the open
Casdoor releases continuously. Here's what landed over the past year, all of it available in Cloud and self-hosted.
A rebuilt admin console
A faster, cleaner console with a command palette, bulk actions, two-column forms and tables where you choose the columns.
Authentication
Magic link sign-in
Users sign in from a one-time link in their inbox, with no password to remember or reset.
Compliance
Audit logs to your SIEM
A new Audit provider forwards sign-in and admin records to Syslog, with retention set per organization.
Sessions
Exclusive sign-in and session limits
Cap concurrent sessions per user, across one app or a whole organization, and see the device, IP and last activity of each.
Enterprise SSO
SAML Single Logout and IdP-initiated SSO
Sign users out of every SAML app at once, and let them start from an identity provider portal.
Authorization
Time-limited, explainable permissions
Permissions can expire on their own, and the console shows which role or group granted each one.
Protocols
Kerberos, DPoP and device login
Windows desktop SSO with Kerberos/SPNEGO, proof-of-possession tokens and the OAuth device flow for TVs and CLIs.
AI agents
MCP authorization and agent registry
Casdoor protects MCP servers, registers AI clients dynamically, exchanges tokens and finds MCP servers on your network.
Security & trust
Security you can verify, not just read about
Identity is the front door to your business. Casdoor is built in the open, so your security team can check exactly how it works instead of trusting a badge.
Found a vulnerability? Please report it privately to admin@casdoor.org.
Open source and auditable
Every line of Casdoor is public on GitHub under Apache-2.0. Review it, scan it or fork it.
Single-tenant by design
Each Casdoor Cloud subscription gets its own Casdoor instance and its own database. No shared tenants.
Data residency
Choose from 23 Cloud regions, or self-host when data must never leave your network.
Phishing-resistant MFA
Passkeys, TOTP and one-time codes, required for a whole organization when you need it.
Abuse protection
Captchas on login and sign-up, rate-limited one-time codes, IP allowlists and session limits.
Keys you control
Tokens signed with your own certificates, configurable lifetimes, DPoP binding and instant revocation.
Complete audit trail
Sign-ins and admin API calls are recorded and can be forwarded to Syslog, your SIEM or a webhook.
HTTPS everywhere
Cloud instances are served over HTTPS with managed certificates, including on custom domains.
Built on open standards
Integrations
Connect to everything
Identity providers, email, SMS, captcha and payment services are added as providers in the console, shared across organizations or kept per organization. No code changes in your apps.
 Google
 GitHub
 Apple
 Facebook
 LinkedIn
 Discord
 GitLab
 Slack
 Telegram
 WeChat
 Entra ID
 Okta
 ADFS
 Azure AD B2C
 Any SAML IdP
 Any OIDC IdP
 Lark
 WeCom
 DingTalk
 SMTP
 SendGrid
 Azure ACS
 Twilio
 Aliyun SMS
 Tencent SMS
 reCAPTCHA
 hCaptcha
 Turnstile
 GeeTest
 Stripe
 PayPal
 Alipay
 WeChat Pay
 uni-app
Developer quickstart
From zero to login in 3 steps
No identity code to write or maintain. Configure Casdoor once and connect every app to it.
Get a Casdoor server
Subscribe to Casdoor Cloud and get your own instance at yourcompany.casdoor.com, or start one yourself with Docker.
docker run -p 8000:8000 casbin/casdoor-all-in-oneCloud instances are set up for you after checkout
Create an application
In the admin console, add an application, set its redirect URL, pick the login methods and providers, and brand the login page.
redirectUris: ["https://app.acme.com/callback"]
providers: ["Google", "GitHub", "SAML"]
Everything is configured in the web console
Connect your app
Use one of the official SDKs, or any standard OIDC, SAML or CAS client library you already have.
npm install casdoor-js-sdk
window.location.href = sdk.getSigninUrl();
Standard protocols, no lock-in
Guides · SDK references · Sample apps on GitHub
Casdoor Cloud pricing
Simple pricing. No per-user fees.
Every plan is a dedicated, fully managed Casdoor instance. Pay a flat price, not per monthly active user.
Starter
For small teams getting started with a hosted Casdoor.
- Dedicated Casdoor instance and database
- OAuth 2.0, OIDC, SAML, CAS, LDAP and SCIM
- Your own subdomain at casdoor.com
- Hosted in Singapore or Japan
- Automatic Casdoor upgrades
- No per-user or per-MAU fees
- Support via tickets
Professional
For growing start-ups that need their own login domain.
- Everything in Starter
- Custom domain with managed TLS certificate
- Choose from 23 regions and switch any time
- 8x5 technical support
Enterprise
For companies running Casdoor in production.
- Everything in Professional
- Priority 8x5 technical support
- Help with onboarding and migration
- Custom terms and invoicing on request
Casdoor for large organizations
Need on-premises deployment, migration help or custom terms?
We help teams plan self-hosted and private-cloud deployments, migrate users from other identity platforms, design authorization models and agree contracts and invoicing that fit your procurement process.
Prefer to run it yourself? Casdoor is free and open source — self-hosting guide.
Prices in USD. Casdoor Cloud is operated by Casbin Inc. See our Terms of Service and Refund Policy.
Cloud or self-hosted
Same Casdoor. You choose who runs it.
| Self-hosted | Casdoor Cloud | |
|---|---|---|
| Price | Free (Apache-2.0) | From $25/month, flat |
| Software | Open-source Casdoor | The same open-source Casdoor |
| Who runs and upgrades it | Your team | We do |
| Region | Your servers or cloud account | 23 regions to choose from (Starter: Singapore or Japan) |
| Domain | Any domain you own | yourcompany.casdoor.com, or your own domain on Professional and Enterprise |
| Database | Your MySQL, PostgreSQL or other database | A dedicated database per instance |
| Support | Community on GitHub and Discord | Tickets or 8x5 support, depending on plan |
| Switch later | Move to Cloud with our help | Export your data and self-host any time |
Casdoor Cloud regions
North America
South America
Europe
Oceania
Middle East
East Asia
Southeast Asia
South Asia
Starter plans run in Singapore or Japan. Professional and Enterprise plans can use any region and switch later.
FAQ
Frequently asked questions
How is Casdoor different from Auth0, Okta or Keycloak?
Can Casdoor secure AI agents and MCP servers?
Can we migrate from Okta, Keycloak or Active Directory?
What's the difference between Casbin and Casdoor?
What's the difference between Casdoor Cloud and the open-source version?
Which regions can I choose?
Do you have SOC 2 or ISO 27001 certification?
Can I move from Cloud to a self-hosted deployment later?
How do billing and cancellation work?
Do you offer consulting, for example on designing authorization?
Ready to secure your next big move?
Put login, single sign-on, MFA, permissions and AI agent access behind one open-source platform, hosted by us or run by you.
Start with Casdoor Cloud
A dedicated instance in the region you choose, from $25/month with no per-user fees.
See plansSelf-host for free
Run the same Apache-2.0 Casdoor on your own servers with Docker or Kubernetes.
Read the docsTalk to an expert
Plan a migration, an on-premises rollout or an authorization model with our team.
Contact sales